Share Infrastructure
Trust administrators and shared systems.
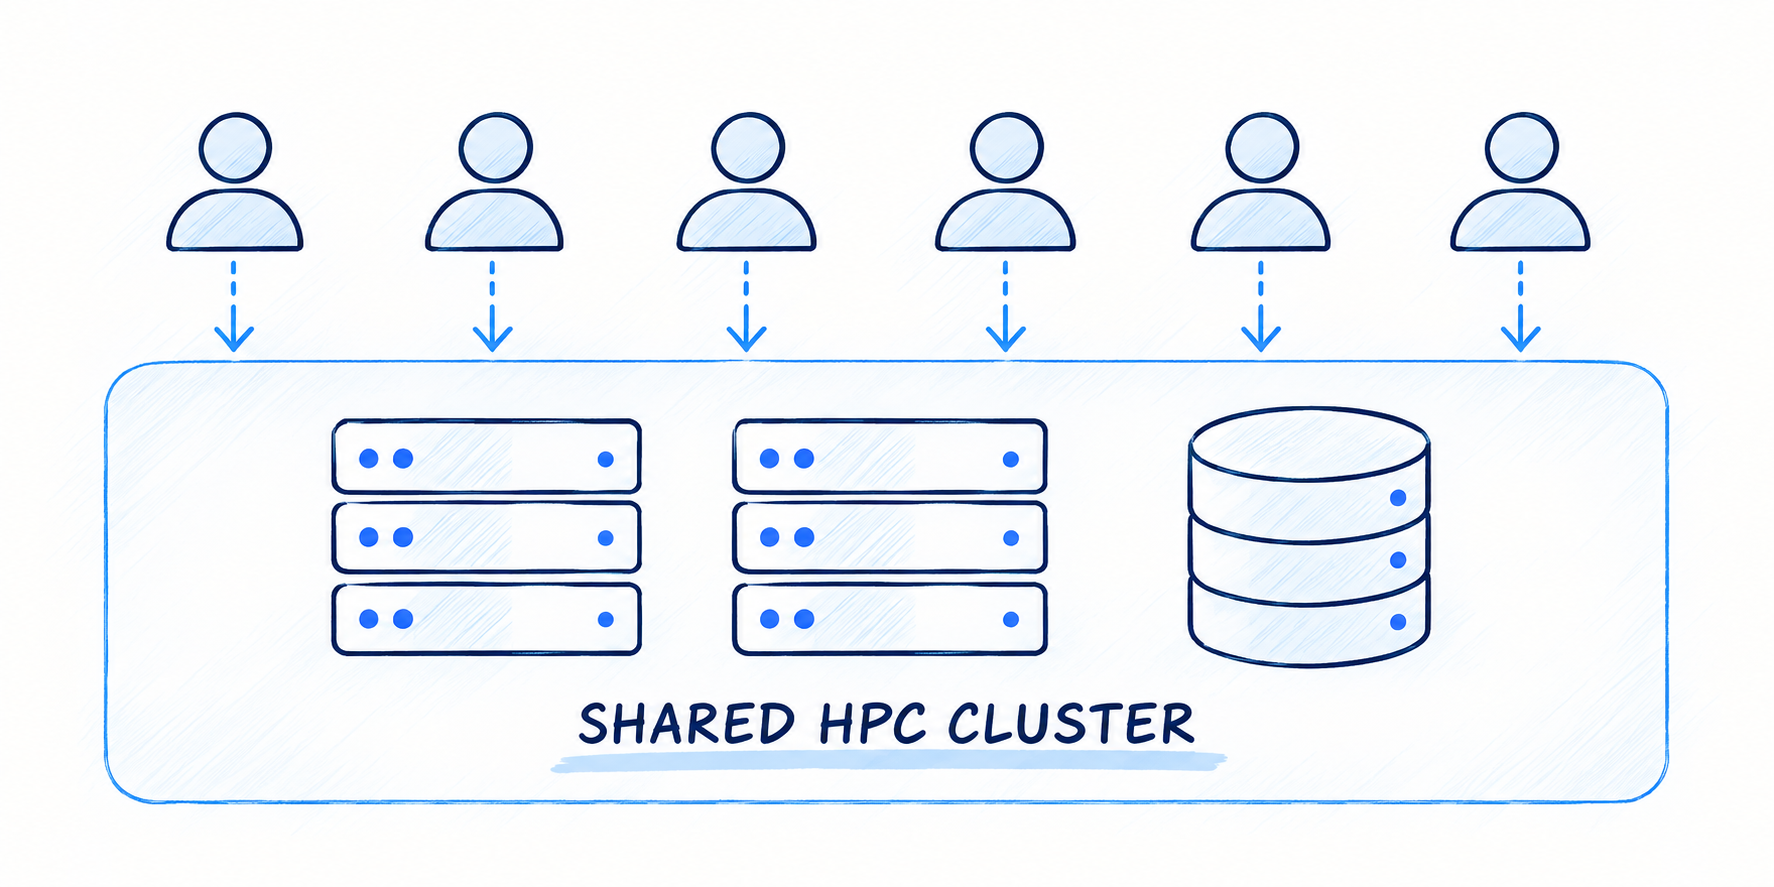
Limited isolation
Risk of data exposure and lateral access.
Run sensitive research workloads on shared HPC infrastructure while keeping every project cryptographically isolated.
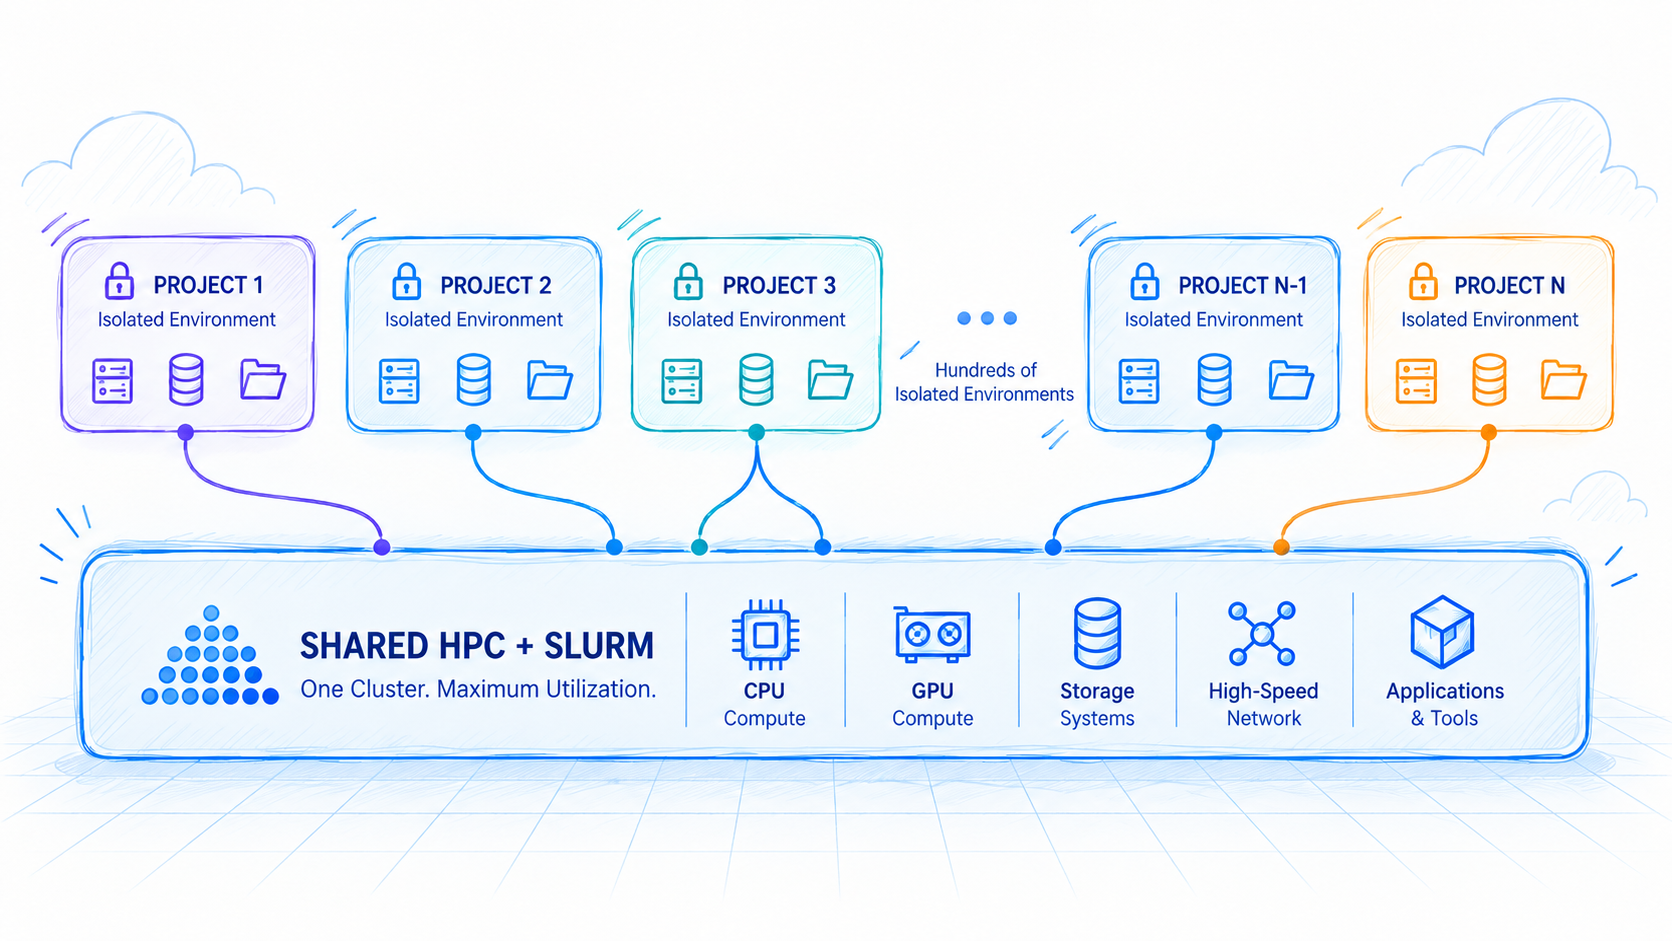
Organizations must choose between convenience or isolation.
Trust administrators and shared systems.
Limited isolation
Risk of data exposure and lateral access.
Duplicate clusters, storage, and administration.
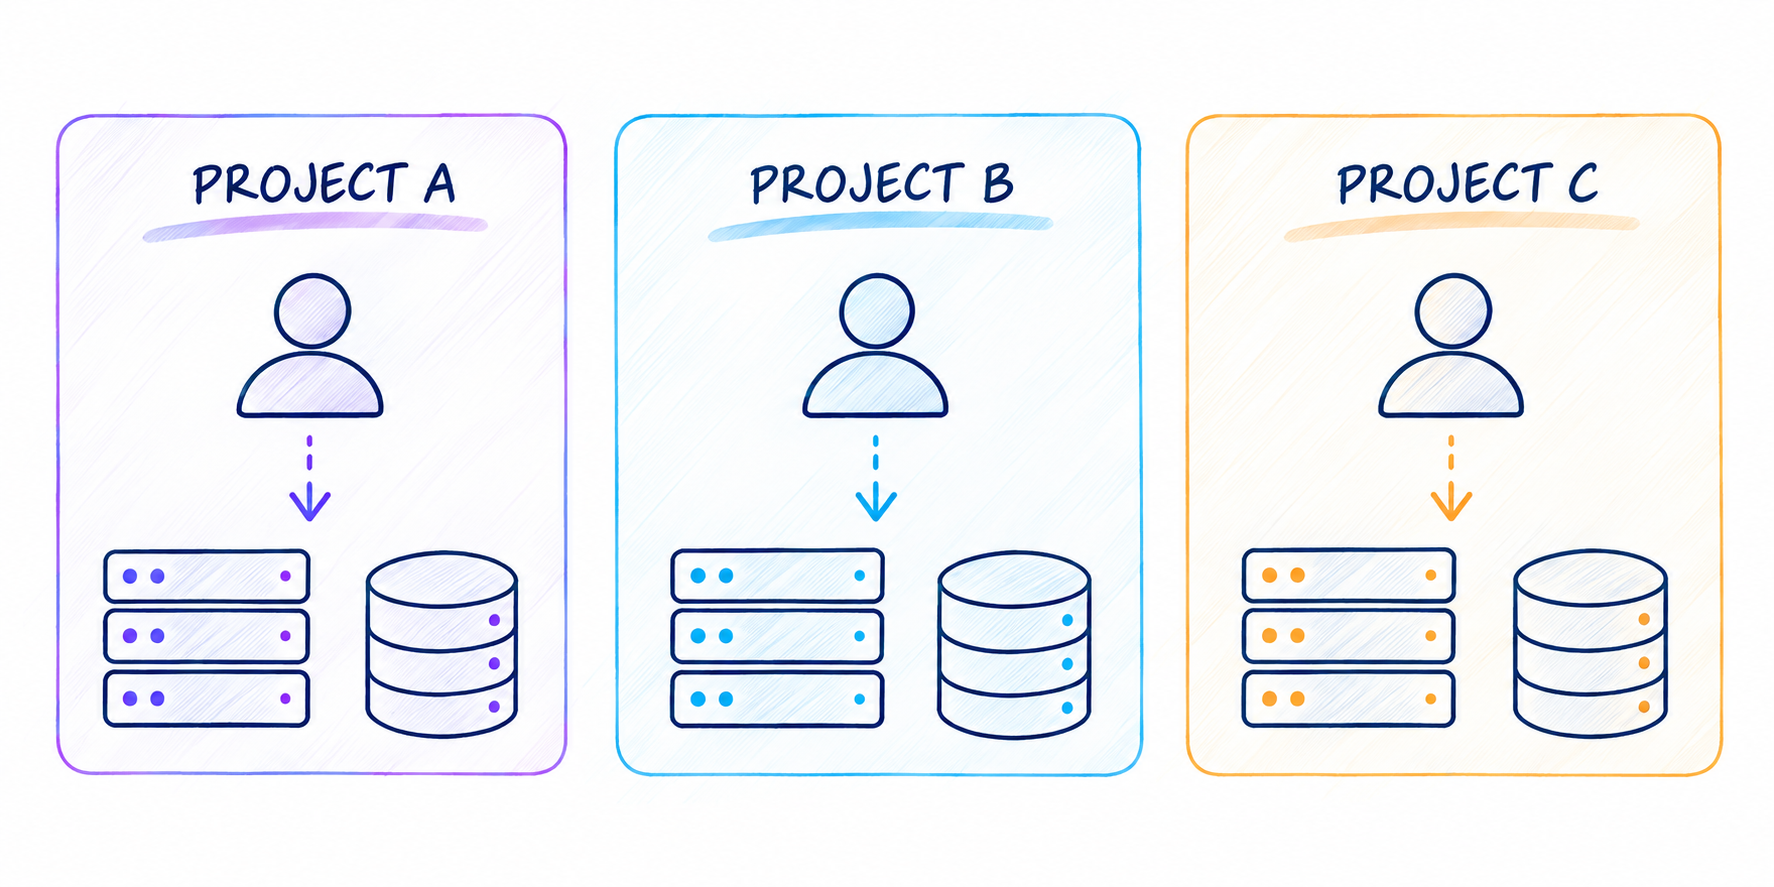
High cost and complexity
Resource duplication and operational overhead.
One shared HPC infrastructure. Cryptographic isolation for every project.
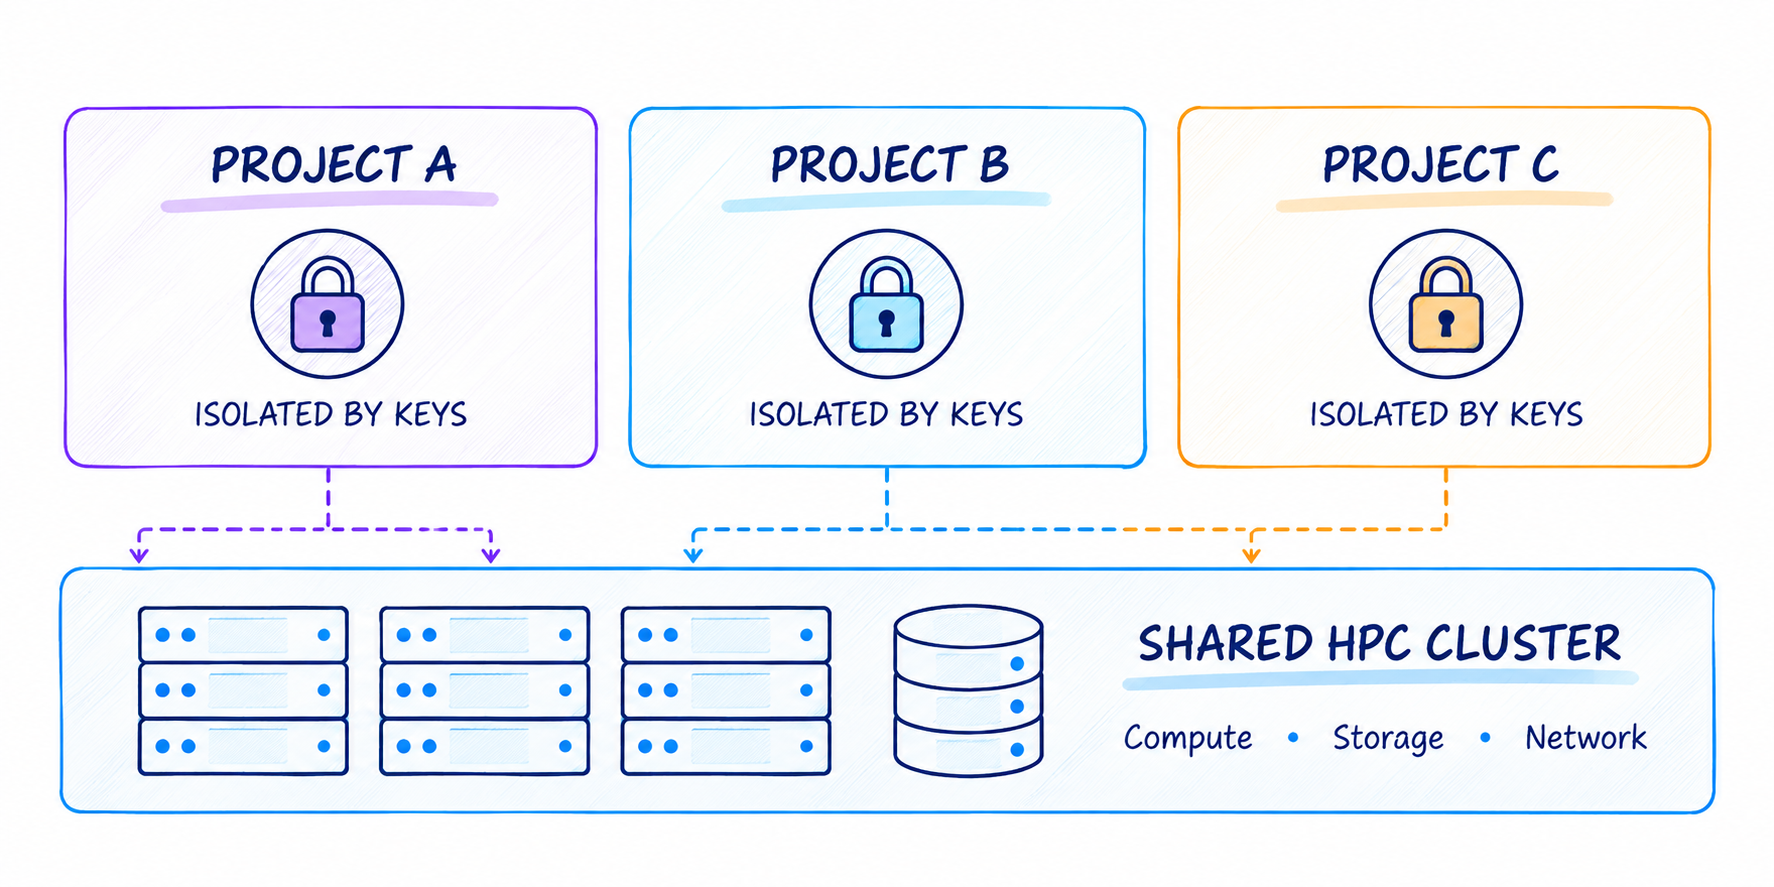
One Cluster
Maximize utilization and reduce cost.
Strong Isolation
Cryptographic boundaries protect every project.
Simplified Operations
Centralized infrastructure without sharing trust.
Cryptographic isolation replaces operational trust.
Trust People + Infrastructure
Trust Cryptography
Researchers securely access HPC, storage, and applications without exposing research data to administrators.
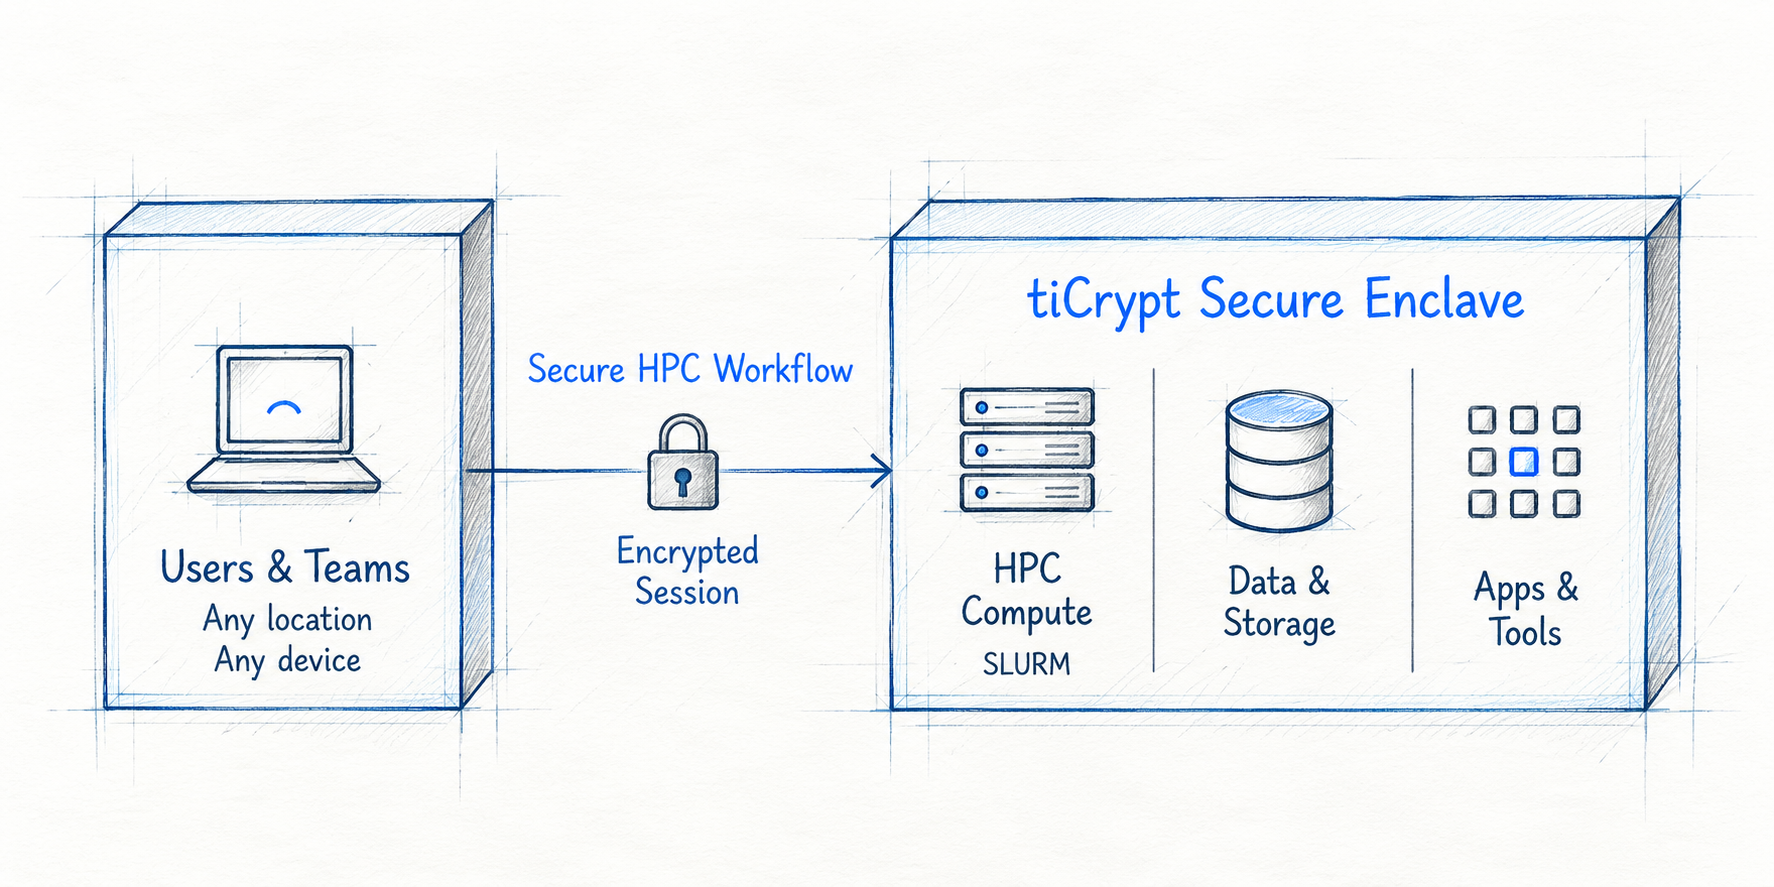
Secure Shared HPC
Give isolated research environments access to shared CPU/GPU resources (GPU - Q4 2026).
Data Stays Protected
Run jobs without moving sensitive data outside the secure environment.
Native SLURM Integration
Use familiar SLURM scheduling and HPC workflows.
Scale Across Programs
Share compute across secure projects.
Maximize Mission Impact
Deliver secure, on-demand HPC performance at enterprise scale, without exposing research data.
Every project gets its own
While sharing
Projects share compute - not trust.
Compromise or misconfiguration in one project cannot expose another.
Scheduler Cannot See Research Data
SLURM handles scheduling - not decryption.
Administrators Cannot Decrypt Files
Researchers retain control of encryption keys.
Endpoints Stay Plaintext-Free
Devices connect without receiving unencrypted research data.
Cryptographic Project Isolation
Each project is isolated by keys, not just policy.
Immutable Audit Trail
Access is logged in tamper-resistant records.
Customer-Controlled Encryption Keys
Your organization controls the keys; tiCrypt cannot access your data.
74 of 110 controls are implemented and managed by tiCrypt, 11 are jointly managed, and 25 remain organizational controls.
TICRYPT MANAGED
74/110
Implemented and managed directly by tiCrypt.
JOINTLY MANAGED
11/110
Shared between tiCrypt capabilities and customer processes.
ORGANIZATIONAL CONTROLS
25/110
Owned by customer policy, governance, and procedures.
11 controls are jointly managed between tiCrypt and the customer, while the remaining 25 organizational controls are addressed through customer policies and procedures.
See the full SSP Blueprint for more information on how compliance is simplified with tiCrypt.
Fully compatible with existing HPC workflows. Researchers, not administrators, control access to research data.
Scheduling
Compute
Research Environments
See how tiCrypt can isolate CUI and ITAR research workloads without replacing your cluster.